Полная инструкция по удалению VirTool:Win32/ExcludeProc.D с зараженного ПК
VirTool:Win32/ExcludeProc.D — действительно очень опасный и неприятный компьютерный вирус, который классифицируется как семейство троянских вредоносных программ. Он может заразить все версии операционной системы на базе Windows, включая XP, Vista, NT, Server, Me, 7, 8 и почти 10. Помимо этой угрозы, он может испортить настройки всего вашего ПК, чтобы вызвать серьезные повреждения. Он имеет возможность отслеживать личную идентификацию пользователя и дает высокий риск, который создает серьезные проблемы внутри вашего ПК. Этот неприятный вирус способен внезапно заразить пользовательскую Систему и достичь высокого уровня безопасности вашего компьютера. Он также имеет возможность создавать множество копий этой инфекции и распространяться по всему компьютеру, чтобы пользователь не смог ее обнаружить. Помимо проникновения в ваш компьютер, он также предлагает другие компьютерные угрозы для проникновения на ваш компьютер и создает множество дополнительных проблем.
Согласно экспертному анализу, если пользователи используют просроченное или взломанное приложение в своей системе, то этот вирус определенно будет обманут вас путем взлома сканера безопасности ложной веб-страницы или уведомления об обновлении. Кроме того, VirTool:Win32/ExcludeProc.D предоставляет бесплатные обновления или запускает процесс сканирования на вашем ПК, что означает, что ваша система будет объединена с множеством других троянских программ.
Каковы негативные действия VirTool:Win32/ExcludeProc.D?
После того, как он полностью обосновался на вашем ПК, этот вирус может взломать ваш работающий веб-браузер, включая Mozilla, Opera, UC, IE, Chrome, Safari и т. д. Сразу после этого он может заменить домашнюю страницу по умолчанию и настройки веб-страницы вашего браузер, чтобы вызвать проблемы с перенаправлением. Он также может перехватывать ваш сеанс просмотра в Интернете, а также нацеливаться на ваше поведение при поиске, чтобы генерировать веб-трафик или даже получать от вас прибыль. Этот хитрый вредоносный вирус также может повредить безопасность вашего брандмауэра и привести к сбою файлов .dll, чтобы вызвать ошибки BSOD в вашей системе. Более того, он может легко отслеживать ваши личные записи, такие как история просмотров, файлы cookie, пароль для входа в систему, данные банковского счета, данные онлайн-транзакций и многое другое. После этого он отправляет всю эту информацию удаленным преступникам, которые могут использовать ее в своих незаконных целях. Вот почему рекомендуется немедленно удалить VirTool:Win32/ExcludeProc.D с вашего компьютера, прежде чем это вызовет дополнительные проблемы в будущем.
Некоторая профилактика для защиты ПК от VirTool:Win32/ExcludeProc.D
- Очень важно регулярно обновлять программное обеспечение безопасности и сканировать ПК проверенным антивирусом.
- Всегда используйте подлинные и лицензированные средства защиты от вредоносных программ.
- Перед установкой любой программы и приложения сначала прочтите лицензионное соглашение с конечным пользователем и его условия.
- Не используйте сторонние ссылки для обновления своего программного обеспечения или приложения.
Обратите внимание:- большинство экспертов по безопасности рекомендуют использовать инструмент безопасности и инструмент для сканирования вредоносных программ, например SpyHunter, для удаления вредоносных программ, а не для ручного процесса. Ручной процесс может быть опасным в ситуации. Пользователи используют этот процесс небрежно. Неосторожное использование ручного процесса может повредить файлы операционной системы, вызвав сбой системы. Именно поэтому многие эксперты по безопасности рекомендуют использовать инструмент безопасности. Кроме того, SpyHunter поставляется с бесплатным сканером вредоносных программ, который позволяет бесплатно сканировать весь компьютер.
Примечание: — VirTool:Win32/ExcludeProc.D — это действительно очень техническая проблема, которая, как думают обычные пользователи. Если вы раздражены и раздражены его злобной деятельностью и раздражением, то вот вам помощь. Ниже мы предлагаем полное решение для эвакуации VirTool:Win32/ExcludeProc.D из вашей зараженной системы. Внимательно прочитайте его и используйте руководство для защиты ПК от нежелательных угроз, таких как VirTool:Win32/ExcludeProc.D.
Для удаления VirTool:Win32/ExcludeProc.D из вашей зараженной системы есть 2 возможных метода:
Лучший и простой трюк для удаления VirTool:Win32/ExcludeProc.D:
VirTool:Win32/ExcludeProc.D создан очень умными программистами (хакерами Black-hat), которые используют очень хитрые коды, которые очень трудно удалить вручную из системы. Поэтому группа хакеров White-hat создает антивирусное программное обеспечение для борьбы с злыми действиями хакеров Black-hat. Средство автоматического удаления лучше всего подходит для удаления VirTool:Win32/ExcludeProc.D из зараженной системы, поскольку оно полностью сканирует вашу систему за несколько минут и находит все проблемы, созданные внутри компьютера. Но, если вы решите использовать процесс удаления вручную, есть много шансов, что вы не сможете искать в каждой папке и VirTool:Win32/ExcludeProc.D остается оставаться внутри ПК. Вот почему, средство автоматического удаления является лучшим вариантом для устранения любой угрозы с ПК, а также будет защищать вашу личность и ПК в будущем. Если вы используете пробную версию антивируса для сканирования на ПК, то вы не будете тратить на это ни копейки.
Руководство по установке автоматического удаления инструмента для:
Прежде всего, нажмите ниже, чтобы загрузить инструмент защиты от вредоносных программ.
Обратите внимание:- большинство экспертов по безопасности рекомендуют использовать инструмент безопасности и инструмент для сканирования вредоносных программ, например SpyHunter, для удаления вредоносных программ, а не для ручного процесса. Ручной процесс может быть опасным в ситуации. Пользователи используют этот процесс небрежно. Неосторожное использование ручного процесса может повредить файлы операционной системы, вызвав сбой системы. Именно поэтому многие эксперты по безопасности рекомендуют использовать инструмент безопасности. Кроме того, SpyHunter поставляется с бесплатным сканером вредоносных программ, который позволяет бесплатно сканировать весь компьютер.
После завершения загрузки сделайте двойной щелчок на загруженном «. exe »файл
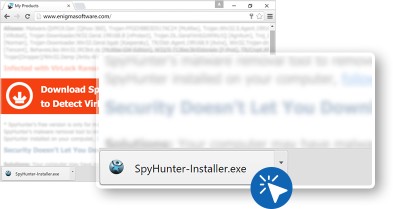
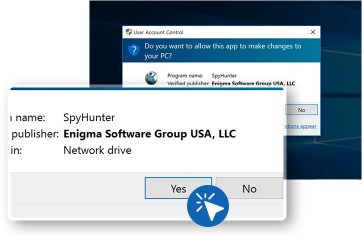
Скорее всего, требуется разрешение « Администратор », если появятся всплывающие окна, нажмите « Да ».
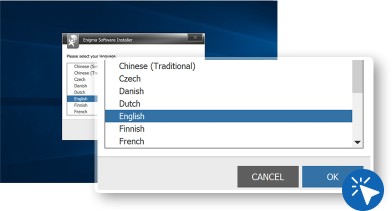
Выберите лучший язык, чтобы легко понять антивирус
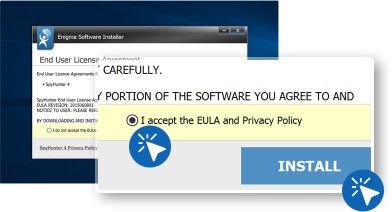
После этого нажмите «Продолжить», а затем примите « Лицензионные соглашения с конечным пользователем ». нажмите кнопку «Установить» .
- Теперь ваш инструмент защиты от вредоносных программ готов к работе.
- Сделайте двойной щелчок на ярлыке антивируса SpyHunter на рабочем столе.
Когда антивирусная программа открыта, она предоставляет вам различные варианты, и первое, что вам нужно сделать, это нажать « Начать новое сканирование »:
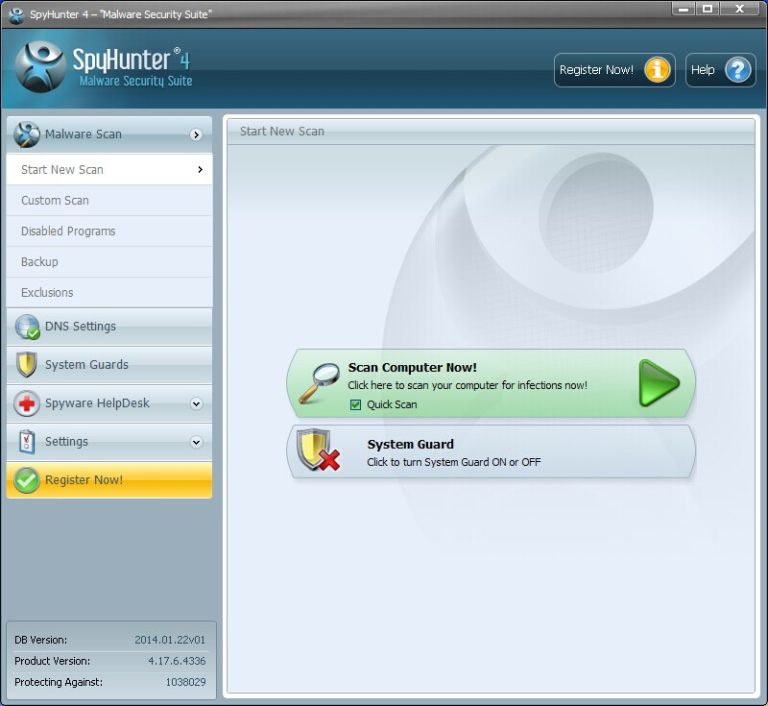
После этого «SpyHunter» начнет сканирование вашей системы на наличие угроз.
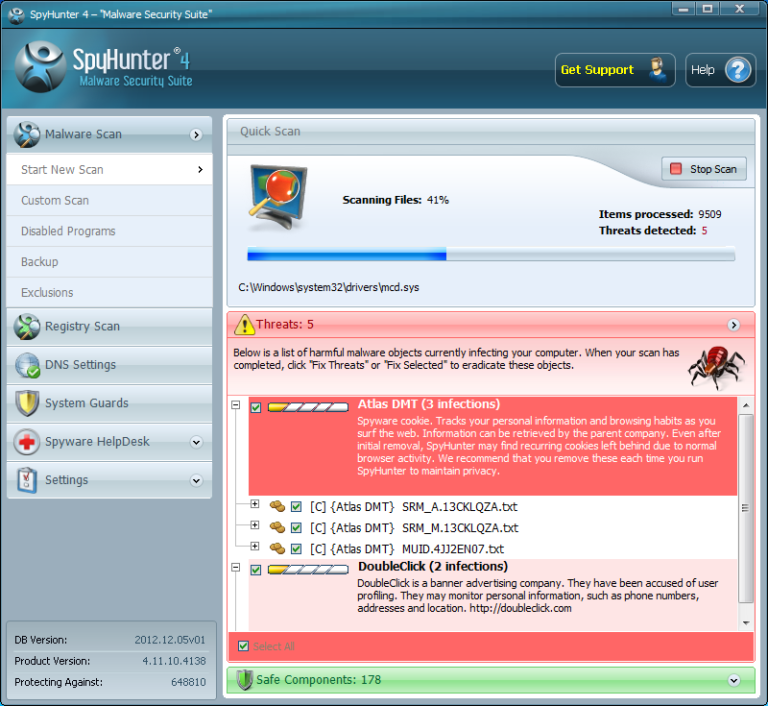
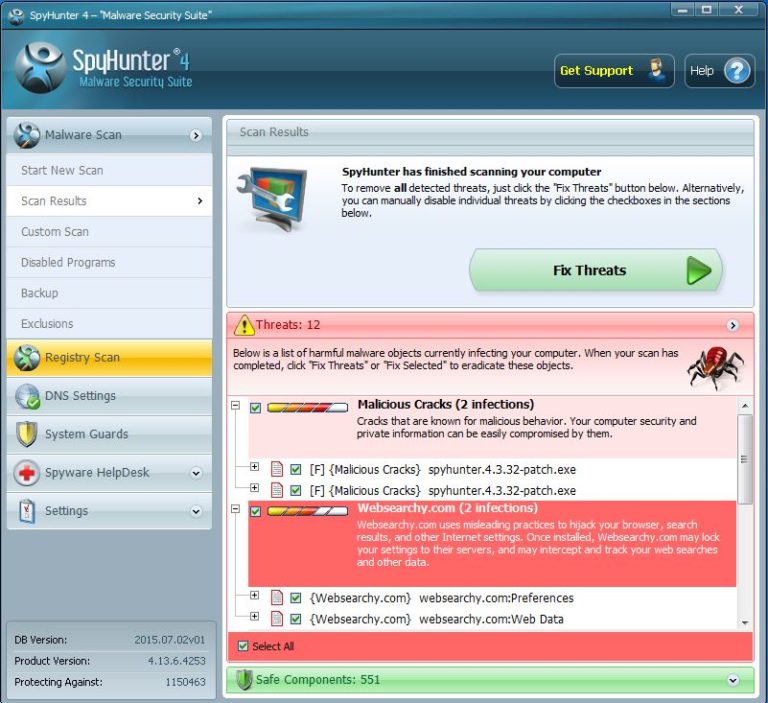
После завершения сканирования вы получите подробную информацию о результатах, а затем нажмите « Устранить угрозы », чтобы удалить имеющиеся угрозы с ПК .
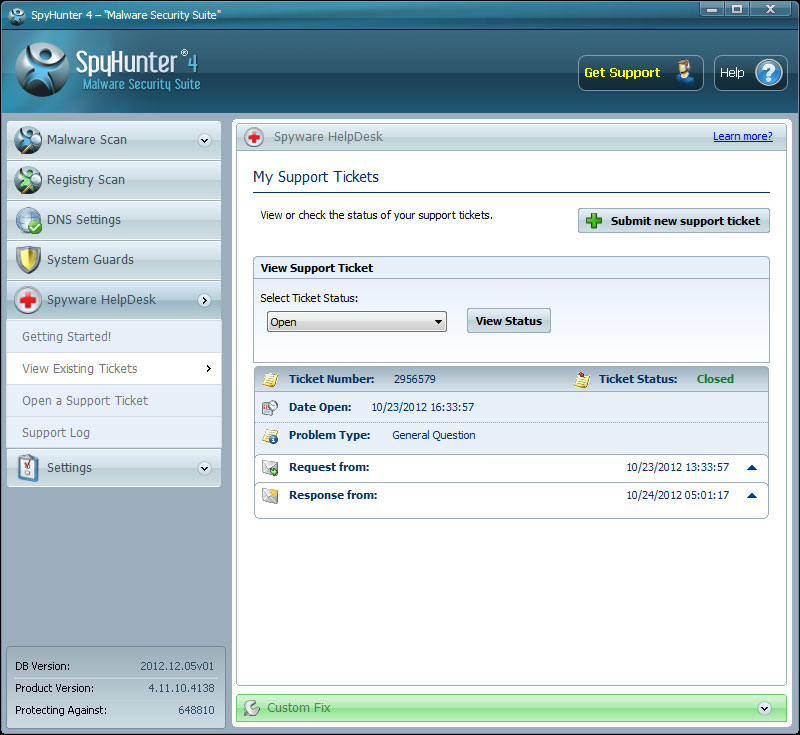
Если вы все еще получаете ошибки в устранении VirTool:Win32/ExcludeProc.D или других вредоносных программ, не паникуйте, SpyHunter предоставит вам « SpyWare HelpDesk », откуда служба технической поддержки поможет вам в решении ваших проблем.
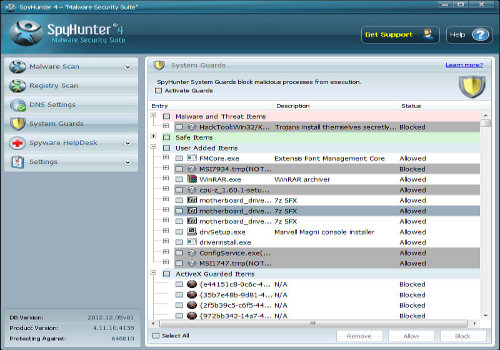
SpyHunter поставляется со встроенным именем брандмауэра как « System Guard », которое защищает вашу систему от предстоящих опасностей.
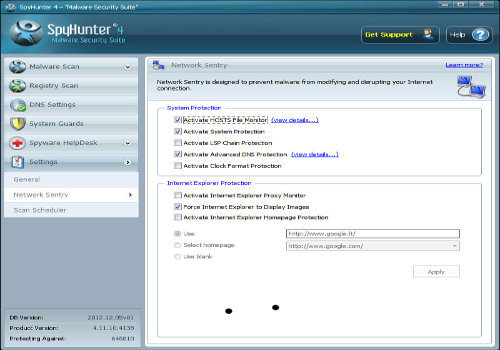
В ходе исследований эксперты по кибербезопасности установили, что все вирусные атаки на компьютерные сети. Таким образом, SpyHunter поставляется с встроенной « Сетевой страж », который защищает все ваше сетевое соединение.
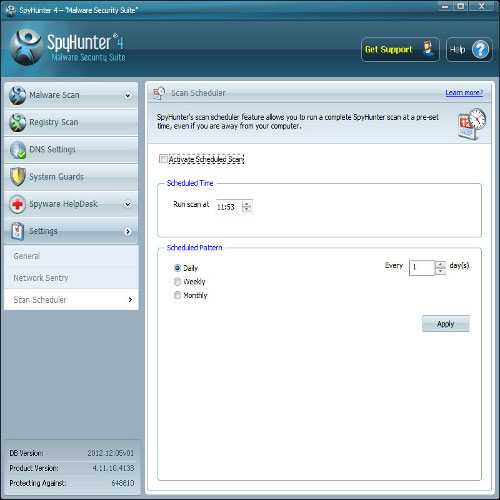
Существует также опция « Расписание сканирования », которая сканирует ваш компьютер к установленному вами времени. Это поможет вам регулярно сканировать ваш компьютер на наличие зараженных файлов или программ, которые попали в порочные пути.
Обратите внимание:- большинство экспертов по безопасности рекомендуют использовать инструмент безопасности и инструмент для сканирования вредоносных программ, например SpyHunter, для удаления вредоносных программ, а не для ручного процесса. Ручной процесс может быть опасным в ситуации. Пользователи используют этот процесс небрежно. Неосторожное использование ручного процесса может повредить файлы операционной системы, вызвав сбой системы. Именно поэтому многие эксперты по безопасности рекомендуют использовать инструмент безопасности. Кроме того, SpyHunter поставляется с бесплатным сканером вредоносных программ, который позволяет бесплатно сканировать весь компьютер.
Техническая процедура для удаления VirTool:Win32/ExcludeProc.D (руководство по устранению VirTool:Win32/ExcludeProc.D):
Черные хакеры — очень умные программисты, они создают свои программы таким образом, чтобы их программы легко скрывались в вашей Системе. VirTool:Win32/ExcludeProc.D может быть удален из вашей системы вручную, если у вас есть четко определенные знания компьютера. Для применения процедуры « Удаление вручную » пользователи / жертвы должны иметь знания по сетям, компьютерным приложениям, реестрам, DNS раздел, и они также должны искать вирус в каждой папке. Вот почему эксперты по безопасности / аналитики предлагают использовать инструмент автоматического удаления, потому что в ручном режиме вы должны тратить свое драгоценное время, если бы вы могли оставить эту работу на инструменте защиты от вредоносных программ, который может искать каждую папку на ПК за несколько минут. В противном случае, если вы все еще хотите использовать ручной процесс и рисковать, ниже приведено руководство по удалению VirTool:Win32/ExcludeProc.D с зараженного компьютера, пройдите его и искорените угрозу с ПК.
Как запустить компьютер в «безопасном режиме»:
Прежде всего, вам необходимо «перезагрузить» вашу систему.
Во время загрузки жертва / пользователь должны несколько раз нажать «F8 ».
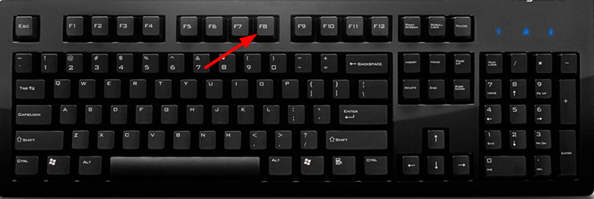
После этого у вас будет возможность выбрать « Безопасный режим », « Безопасный режим с поддержкой сети » и « Безопасный режим с командной строкой ». Вы должны выбрать « Безопасный режим с поддержкой сети ».
Когда ваша система загружается в безопасном режиме, вы должны открыть диспетчер задач, чтобы уничтожить все нежелательные процессы, запущенные VirTool:Win32/ExcludeProc.D
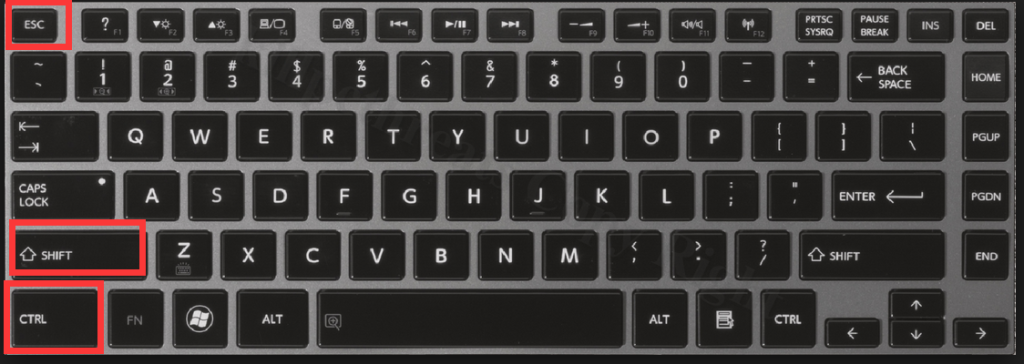
Для открытия « Диспетчера задач » пользователи должны нажать одновременно « Ctrl + Shift + Esc ».
Узнайте нежелательный процесс или приложение, в котором у вас есть сомнения или связанные с VirTool:Win32/ExcludeProc.D.
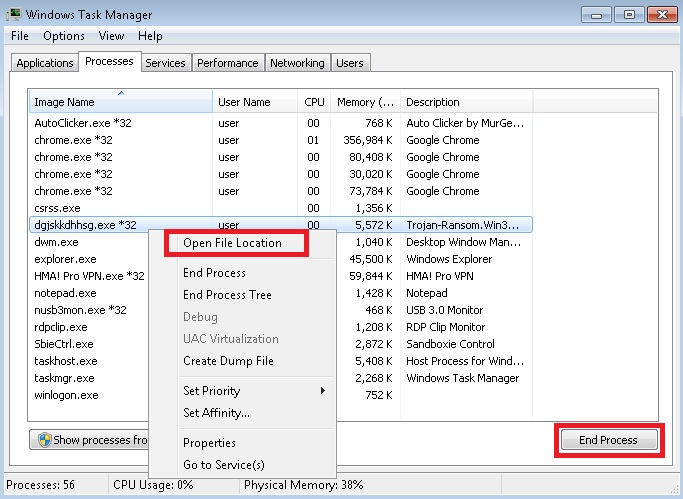
- После нахождения вредоносных программ нажмите [ Завершить процесс ].
- Вы также можете записать местоположение процесса, чтобы вы могли легко удалить его. Для этого вам нужно щелкнуть правой кнопкой мыши по следующему процессу, а затем нажать « Открыть местоположение файла » после этого местоположения заметки.
- Теперь вам нужно открыть команду [ Run ], чтобы щелкнуть вместе « Windows logo + R », а затем ввести следующую позицию VirTool:Win32/ExcludeProc.D в команде«Run» и удалить ее навсегда.
Обратите внимание:- большинство экспертов по безопасности рекомендуют использовать инструмент безопасности и инструмент для сканирования вредоносных программ, например SpyHunter, для удаления вредоносных программ, а не для ручного процесса. Ручной процесс может быть опасным в ситуации. Пользователи используют этот процесс небрежно. Неосторожное использование ручного процесса может повредить файлы операционной системы, вызвав сбой системы. Именно поэтому многие эксперты по безопасности рекомендуют использовать инструмент безопасности. Кроме того, SpyHunter поставляется с бесплатным сканером вредоносных программ, который позволяет бесплатно сканировать весь компьютер.
Очень важно удалить VirTool:Win32/ExcludeProc.D или другие нежелательные файлы из ОС Windows:
Для удаления VirTool:Win32/ExcludeProc.D из Windows Vista, XP, 7, 8 или 8.1 следуйте приведенным ниже инструкциям.
Прежде всего, вы должны нажать на кнопку « Пуск », которая отличается в разных версиях, но вы легко можете ее найти.
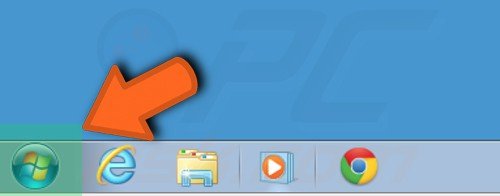
После нажатия на кнопку « Windows START », вы должны найти « Панель управления ». Вы можете искать об этом.
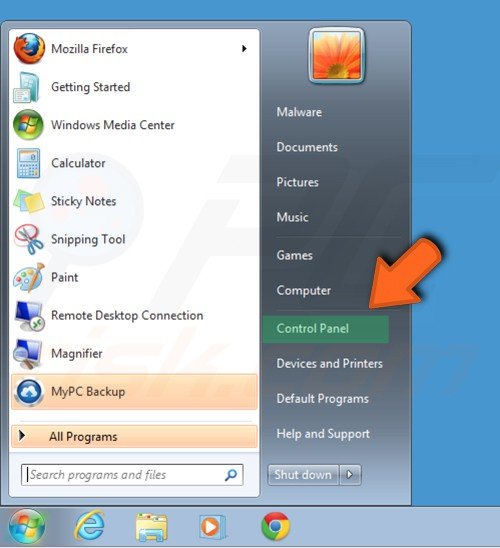
Когда вы находитесь внутри « Панели управления », вы получите много вариантов там, где вы должны найти « Программы и функции » и нажать на нее.
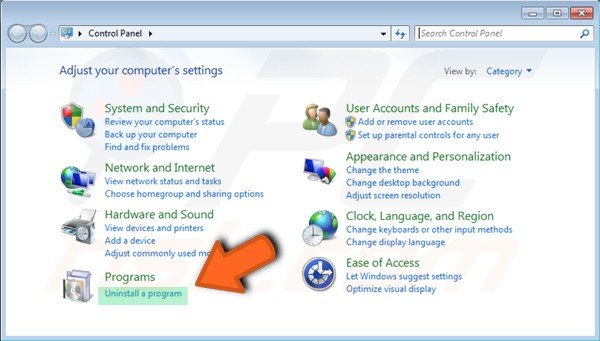
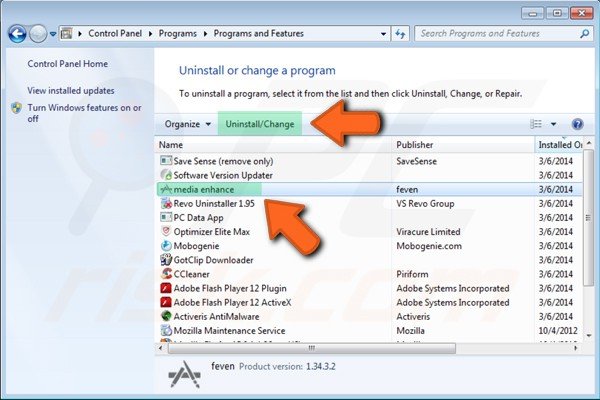
И теперь вам нужно найти неизвестные программы или VirTool:Win32/ExcludeProc.D. затем выберите элемент и нажмите « Удалить / Изменить ».
Но если вы используете «Windows 10», то есть другой способ удалить VirTool:Win32/ExcludeProc.D:
Прежде всего, нажмите кнопку «СТАРТ» в Windows , а затем выполните поиск «Настройки».
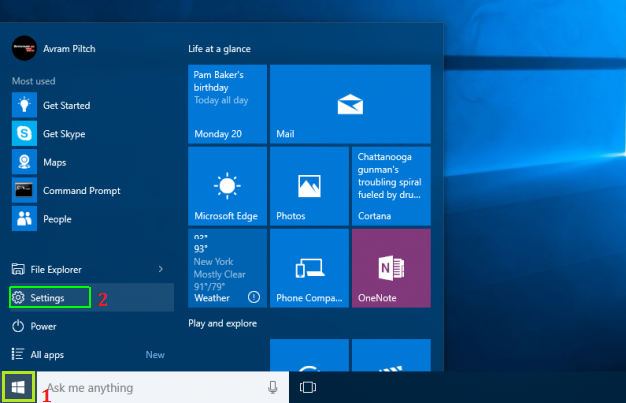
Когда вы находитесь в «Настройки», нажмите «Система».
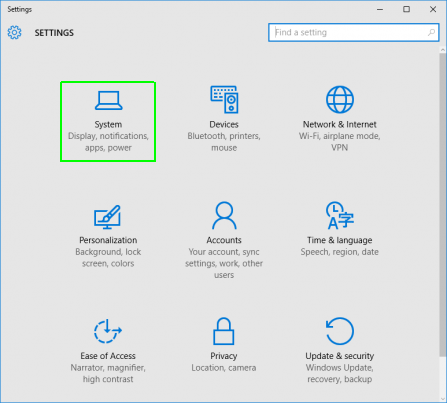
В системе найдите « Приложения и функции » и нажмите на нее.
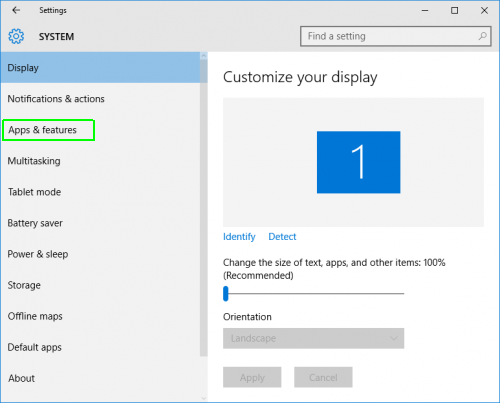
В « Приложениях и функциях » вы должны найти все вредоносные элементы и VirTool:Win32/ExcludeProc.D, а затем нажать «Удалить».
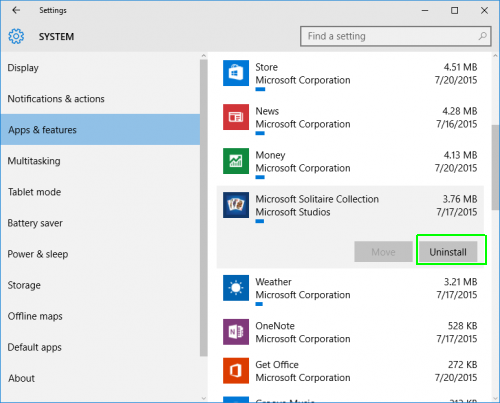
Теперь вредоносное приложение удаляется из Системы.
Обратите внимание:- большинство экспертов по безопасности рекомендуют использовать инструмент безопасности и инструмент для сканирования вредоносных программ, например SpyHunter, для удаления вредоносных программ, а не для ручного процесса. Ручной процесс может быть опасным в ситуации. Пользователи используют этот процесс небрежно. Неосторожное использование ручного процесса может повредить файлы операционной системы, вызвав сбой системы. Именно поэтому многие эксперты по безопасности рекомендуют использовать инструмент безопасности. Кроме того, SpyHunter поставляется с бесплатным сканером вредоносных программ, который позволяет бесплатно сканировать весь компьютер.
Все вредоносные программы или VirTool:Win32/ExcludeProc.D могут изменить ваш DNS-адрес, чтобы перенаправить ключевые слова для поиска на спонсируемый сайт:
Для безопасного просмотра вы должны заблокировать все перенаправления и для этого следуйте инструкциям.
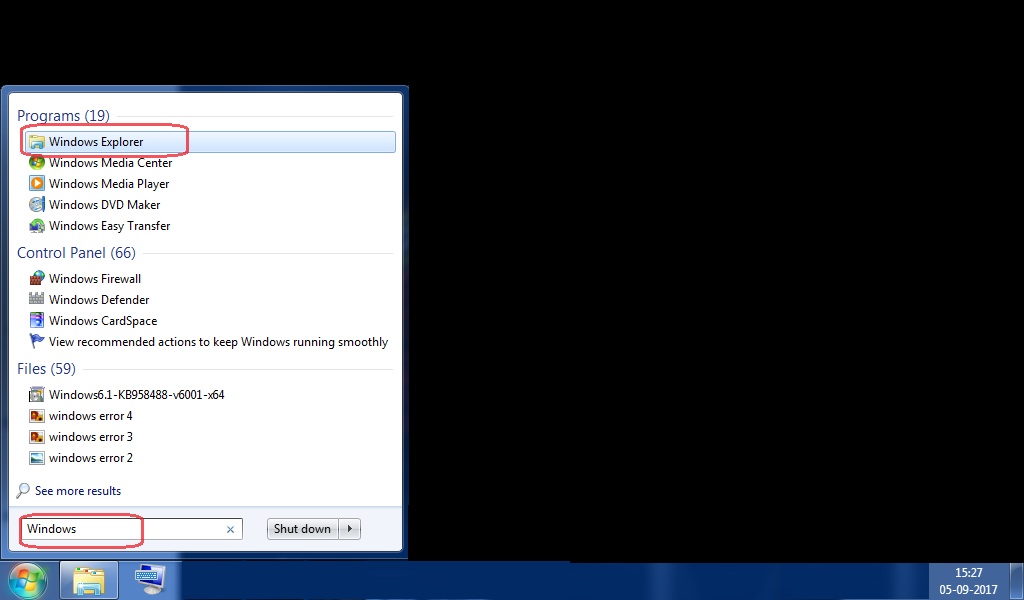
Прежде всего откройте Windows Explorer. Прежде всего открытый проводник Windows. Найдите этот адрес папки C:// Windows/System32/drivers/etc/Host.
Если ваша Система заражена VirTool:Win32/ExcludeProc.D или другим вредоносным ПО, есть вероятность, что в этом разделе будет добавлено много нежелательных IP-адресов.
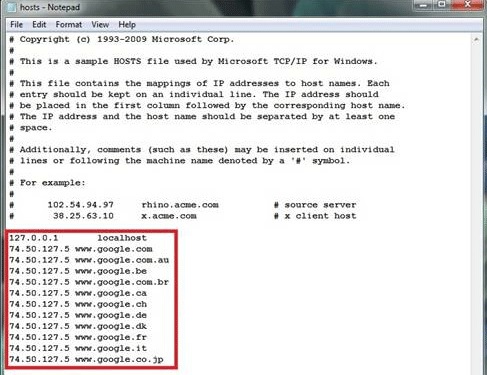
После этого вам нужно удалить все нежелательные IP-адреса, но не удалять записи локального хоста.
После удаления всех нежелательных IP-адресов сохраните файл и выйдите из проводника Windows.
После очистки файла хоста теперь вы можете легко сбросить настройки DNS:
Для сброса настроек DNS вам необходимо перейти в « Панель управления »;
Как только вы окажетесь в « Панели управления », найдите « Центр управления сетями и общим доступом » или « Опции сети ».
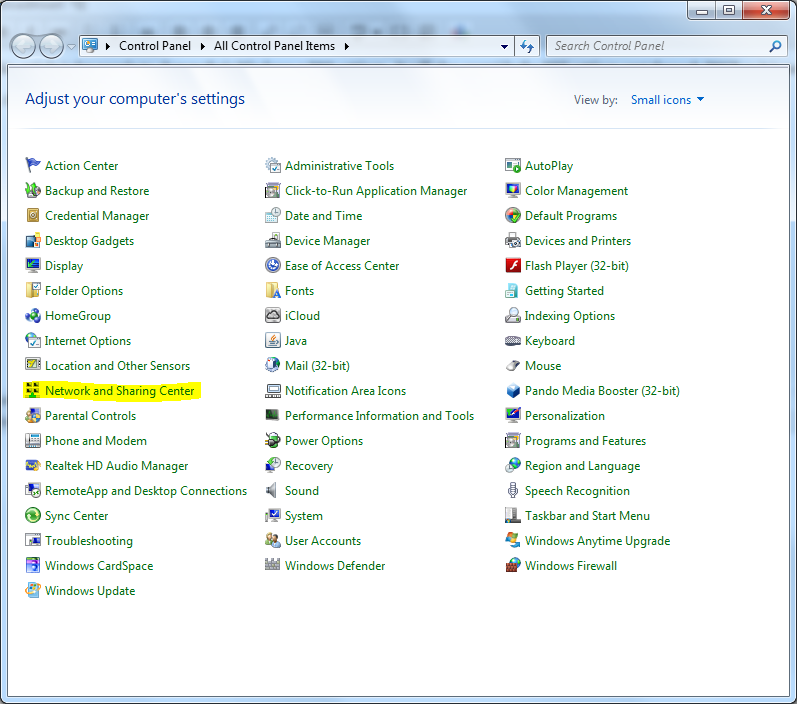
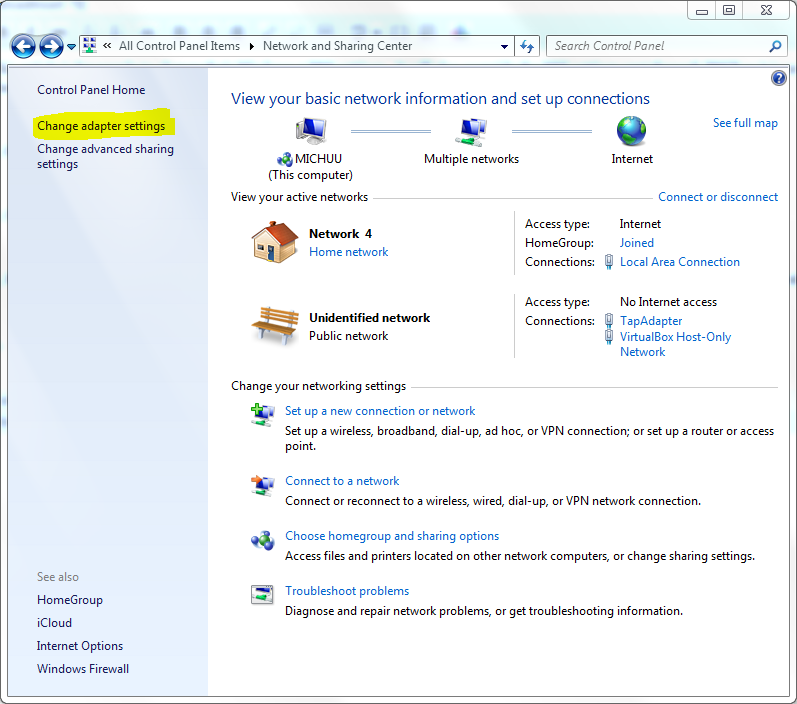
Внутри « Центра управления сетями и общим доступом » вы должны найти « Изменить настройки адаптера » (вы найдете его на левой боковой панели).
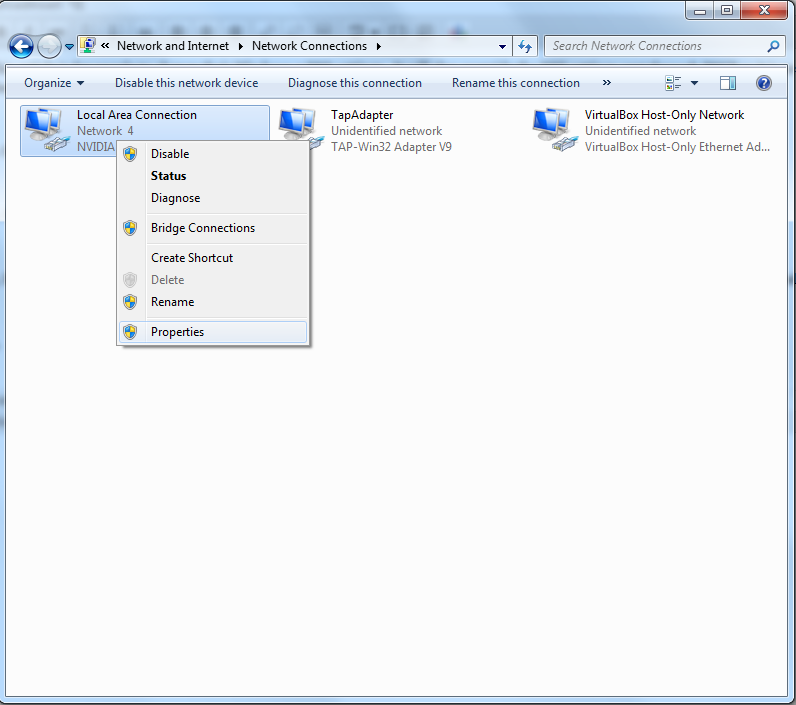
В « Настройках адаптера » вы получите всю сеть, связанную с вашим устройством. Сделайте « Правый клик » на « Имя сетевого устройства » и выберите «Свойства».
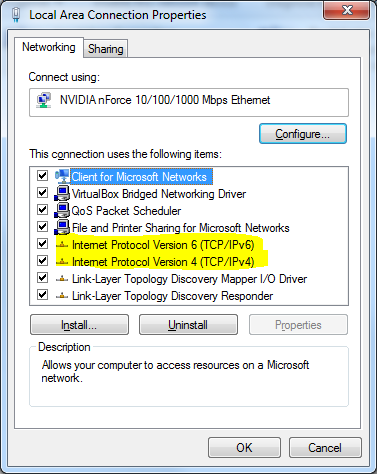
Когда вы находитесь в «Свойствах», выберите « IP-версию » для DNS и затем снова нажмите «Свойства» .
После нажатия на кнопку «Свойства» в всплывающем окне в этом окне вы должны нажать на «Дополнительно» вариант.
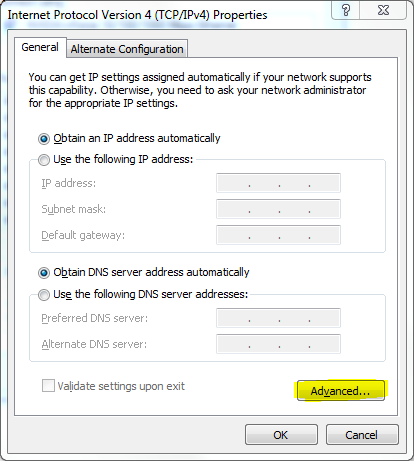
В разделе «Дополнительно» вы найдете DNS, в верхних вкладках кликните по нему.
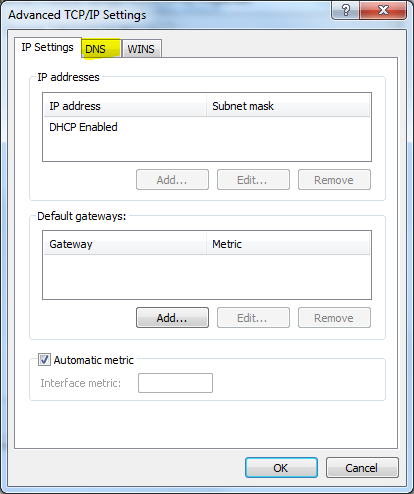
В разделе «DNS» вы должны нажать «Добавить», затем ввести « IP-адрес сервера Tier2 » и снова нажать « Добавить» .
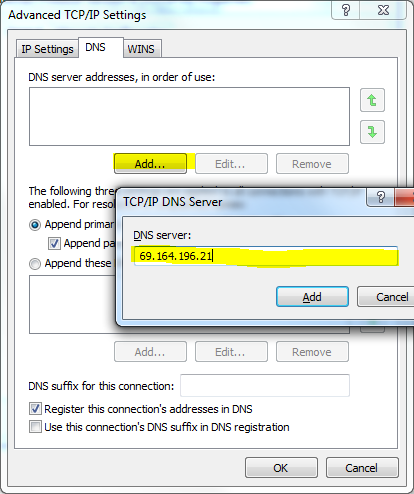
Для получения более подробной информации о «IP-адресе сервера Tier2» вы можете бесплатно посетить [https://www.opennicproject.org/nearest-servers/]. На этом сайте вы получите всю информацию об IP-адресах.
«Ради вашего блага, мы хотели бы сообщить, что используйте эти шаги только в том случае, если вы знаете об этом, иначе вы испортите системные файлы и потеряете свою руку из вашей системы. Вместо того, чтобы тратить свое драгоценное время, используйте программу защиты от вредоносных программ, которая защищает ваш компьютер и экономит время ».
Обратите внимание:- большинство экспертов по безопасности рекомендуют использовать инструмент безопасности и инструмент для сканирования вредоносных программ, например SpyHunter, для удаления вредоносных программ, а не для ручного процесса. Ручной процесс может быть опасным в ситуации. Пользователи используют этот процесс небрежно. Неосторожное использование ручного процесса может повредить файлы операционной системы, вызвав сбой системы. Именно поэтому многие эксперты по безопасности рекомендуют использовать инструмент безопасности. Кроме того, SpyHunter поставляется с бесплатным сканером вредоносных программ, который позволяет бесплатно сканировать весь компьютер.
Когда ваш компьютер заражается любой вредоносной угрозой, такой как VirTool:Win32/ExcludeProc.D, он создает поддельные записи реестра и многое другое.
Как удалить поддельные записи реестра из зараженной системы:
Для того, чтобы надежно удалить поддельный реестр , созданный VirTool:Win32/ExcludeProc.D первых пользователей должны удалить скрытые файлы из VirTool:Win32/ExcludeProc.D:
Для этого необходимо открыть « Панель управления ».
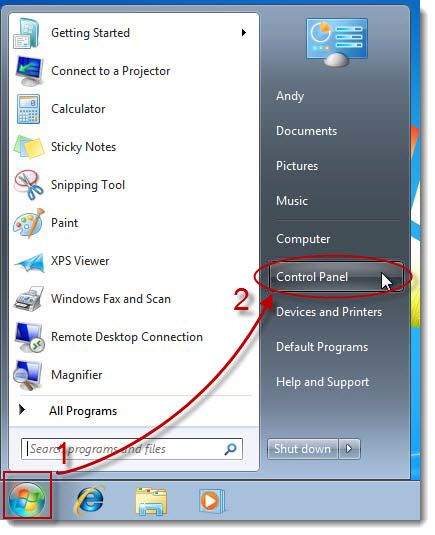
В разделе « Панель управления » необходимо нажать « Внешний вид и персонализация ».
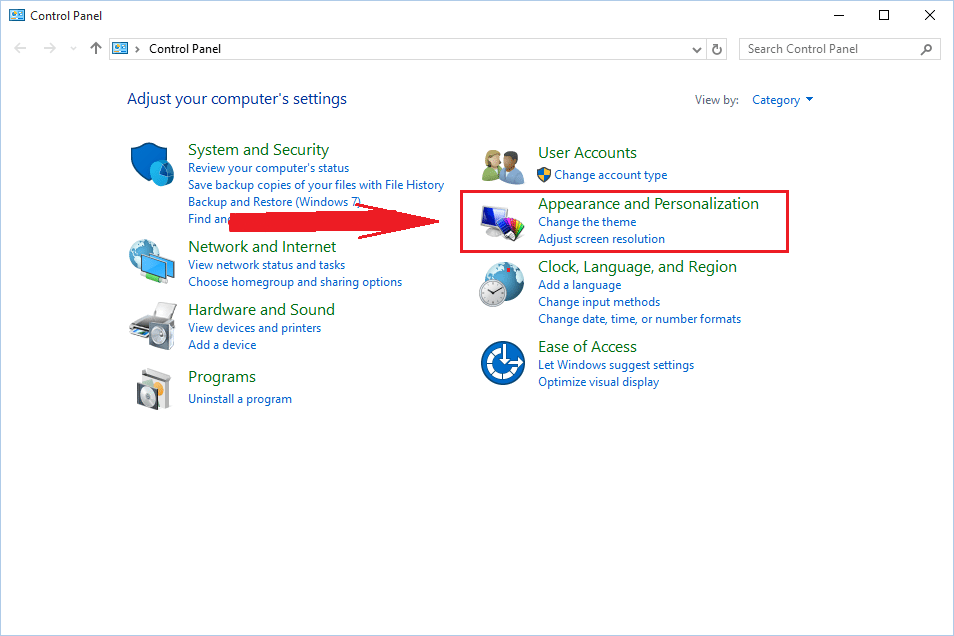
В « Внешний вид и персонализация » найдите « Папка вариант », нажмите на нее. После этого в этом окне появится всплывающее окно, нажмите на вкладку «Вид» .
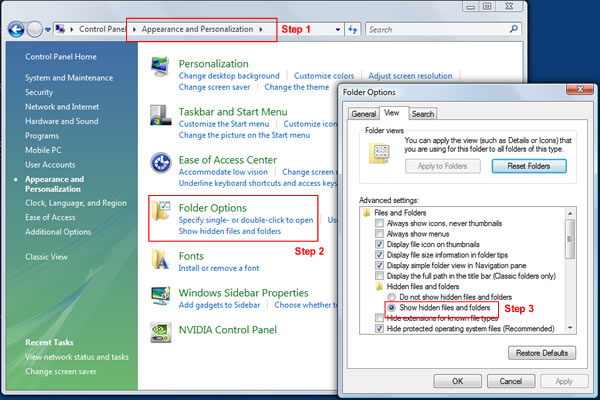
- Выберите « Показать скрытые файлы и папки », это поможет вам показать все скрытые файлы и папки, доступные в системе.
- Теперь для проверки всех скрытых файлов перейдите в следующие файлы [C: \ Users \ имя пользователя \ AppData \ Local \ Temp] .
- Удалите все доступные файлы и папки в папке Temp. (может потребоваться разрешение администратора, затем просто нажмите «Продолжить».)
Теперь мы готовы удалить реестр, созданный VirTool:Win32/ExcludeProc.D из системы:
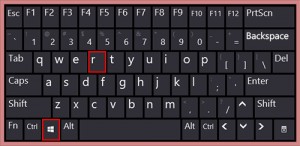
Чтобы открыть редактор реестра, сначала нужно открыть команду «RUN» , для этого нажмите кнопку « Windows logo + R ».
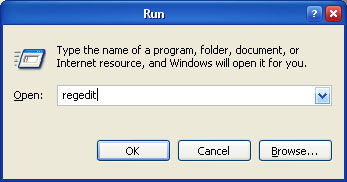
В поле «RUN» необходимо ввести «regedit», эта команда откроет редактор реестра Windows.
Сразу после ввода «regedit» откроется новое окно с именем «Редактор реестра Windows».
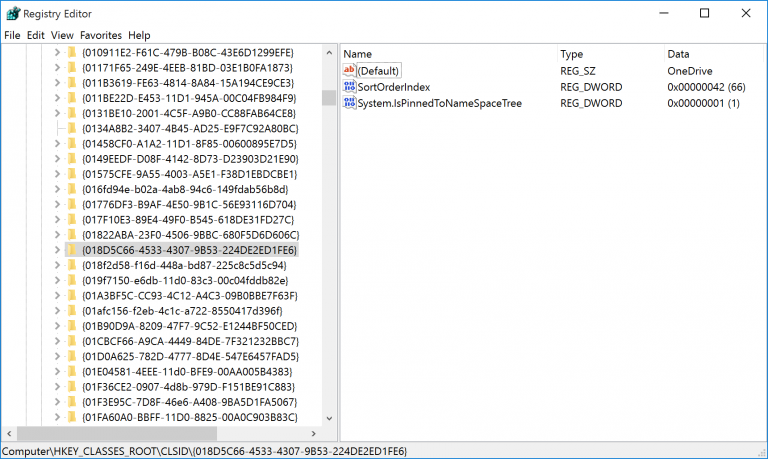
Жертвы должны открыть каждый ящик и удалить оттуда VirTool:Win32/ExcludeProc.D или связанные с ним записи реестра.
Вот некоторые распространенные файлы реестра, зараженные VirTool:Win32/ExcludeProc.D:
[HKEY_CURRENT_USER \ Software \ Microsoft \ Windows \ CurrentVersion \ Explorer \ Папки оболочки]
Startup = «C: \ windows \ start menu \ Programs \ startup»
[HKEY_CURRENT_USER \ Software \ Microsoft \ Windows \ CurrentVersion \ Explorer \ Папки пользовательских оболочек]
Startup = «C: \ windows \ start menu \ Programs \ startup»
[HKEY_LOCAL_MACHINE \ Software \ Microsoft \ Windows \ CurrentVersion \ explorer \ Папки пользовательских оболочек]
«Common Startup» = «C: \ windows \ меню пуска \ программы \ автозагрузка»
[HKEY_LOCAL_MACHINE \ Software \ Microsoft \ Windows \ CurrentVersion \ explorer \ Папки оболочки]
«Common Startup» = «C: \ windows \ меню пуска \ программы \ автозагрузка»
HKEY_LOCAL_MACHINE \ Software \ Microsoft \ Windows \ CurrentVersion \ RunServices]
«Whwhat» = «c: \ runfolder \ [Malware] .exe «
[HKEY_LOCAL_MACHINE \ Software \ Microsoft \ Windows \ CurrentVersion \ RunServicesOnce]
«Whwhat» = «c: \ runfolder \ [Malware] .exe «
[HKEY_LOCAL_MACHINE \ Software \ Microsoft \ Windows \ CurrentVersion \ Run]
«Whwhat» = «c: \ runfolder \ [Malware] .exe «
[HKEY_LOCAL_MACHINE \ Software \ Microsoft \ Windows \ CurrentVersion \ RunOnce]
«Whwhat» = «c: \ runfolder \ [Malware] .exe «
[HKEY_CURRENT_USER \ Software \ Microsoft \ Windows \ CurrentVersion \ Run]
«Whwhat» = «c: \ runfolder \ [Malware] .exe «
[HKEY_CURRENT_USER \ Software \ Microsoft \ Windows \ CurrentVersion \ RunOnce]
«Whwhat» = «c: \ runfolder \ [Malware] .exe «
[HKEY_CURRENT_USER \ Software \ Microsoft \ Windows \ CurrentVersion \ RunServices]
«Whwhat» = «c: \ runfolder \ [Malware] .exe «
[HKEY_CLASSES_ROOT \ exefile \ shell \ open \ command] @ = «\»% 1 \ «% *»
[HKEY_CLASSES_ROOT \ comfile \ shell \ open \ command] @ = «\»% 1 \ «% *»
[HKEY_CLASSES_ROOT \ batfile \ shell \ open \ command] @ = «\»% 1 \ «% *»
[HKEY_CLASSES_ROOT \ htafile \ Shell \ Open \ Command] @ = «\»% 1 \ «% *»
[HKEY_CLASSES_ROOT \ piffile \ shell \ open \ command] @ = «\»% 1 \ «% *»
[HKEY_LOCAL_MACHINE \ Software \ CLASSES \ batfile \ shell \ open \ command] @ = «\»% 1 \ «% *»
[HKEY_LOCAL_MACHINE \ Software \ CLASSES \ comfile \ shell \ open \ command] @ = «\»% 1 \ «% *»
[HKEY_LOCAL_MACHINE \ Software \ CLASSES \ exefile \ shell \ open \ command] @ = «\»% 1 \ «% *»
[HKEY_LOCAL_MACHINE \ Software \ CLASSES \ htafile \ Shell \ Open \ Command] @ = «\»% 1 \ «% *»
[HKEY_LOCAL_MACHINE \ Software \ CLASSES \ piffile \ shell \ open \ command] @ = «\»% 1 \ «% *»
Обратите внимание:- большинство экспертов по безопасности рекомендуют использовать инструмент безопасности и инструмент для сканирования вредоносных программ, например SpyHunter, для удаления вредоносных программ, а не для ручного процесса. Ручной процесс может быть опасным в ситуации. Пользователи используют этот процесс небрежно. Неосторожное использование ручного процесса может повредить файлы операционной системы, вызвав сбой системы. Именно поэтому многие эксперты по безопасности рекомендуют использовать инструмент безопасности. Кроме того, SpyHunter поставляется с бесплатным сканером вредоносных программ, который позволяет бесплатно сканировать весь компьютер.
Компьютер / ПК Эксперты руководство по безопасности ПК от VirTool:Win32/ExcludeProc.D:
Учитывая все обстоятельства, единственный величайший фактор в сохранении такой опасности, как болезнь VirTool:Win32/ExcludeProc.D, лежит на вас. Действительно, даже вы на данный момент внедряете Anti-Malware, и вы проверяете свой компьютер удобным, если у вас нет шансов быть преднамеренно направленным на ваш ПК при его использовании. Это ясно, чтобы заразиться VirTool:Win32/ExcludeProc.D еще раз. В соответствии с этим, вам просто необходимо соблюдать осторожность, чтобы не подвергаться влиянию риска в будущем, и несколько указаний и рекомендаций, указанных здесь, в идеале, сохранят ваш компьютер от заражения в ближайшее время.
- Постоянно обновляйте антивирусные программы.
- Используйте надежные пароли для важных данных, чтобы избежать взлома.
- Выведите из строя емкости автоматического запуска для загруженных документов и вставленных дисков.
- Квадратное автоматическое обновление от организации внутри системы.
- Забудьте о неясных бенефициарных электронных письмах.
- Воздерживаться от взаимодействия с открытым исходным кодом, как Wi-Fi.
- Используйте брандмауэр на основе оборудования, чтобы обезопасить систему от загрязнения.
- Отправьте страховку DNS от естественного изменения.
- Используйте расширение и программирование рекламного блокиратора, помня о конечной цели серфинга, без каких-либо дополнительных рекламных акций и уведомлений о мусоре
- Старайтесь не использовать какие-либо ненадежные или неофициальные области для просмотра и загрузки записей в браузере.
Благодарим Вас за посещение нашего сайта, мы надеемся, что вы получили ваше решение.
Для любой другой информации или предложения, не стесняйтесь связаться с нами.
Специальное предложение: Spyhunter Anti-Malware
EnigmaSoft предлагает бесплатный пробный период в течение 7 дней с помощью средства защиты от вредоносных программ Spyhunter (Windows) & (MAC) операционной системы.
VirTool:Win32/ExcludeProc.C Removal Process

VirTool:Win32/ExcludeProc.C is kind of Trojan brings problems to your PC. It generally appears on computer silently, and if there is no special application, you could not detect it. Even for many time it has got inside on your PC, you have no chance to make sense of it. That is to say, it could pretend itself very well.
VirTool:Win32/ExcludeProc.C is good at camouflaging itself so that nobody may recognize it and delete it. Furthermore, its immaculate target is not for the sake of entertainment, instead all these conducts are for money. How may it do that? There are for the most part two ways, one is immediate to evoke money from you, and the other is to make benefits by your data.
For the previous, VirTool:Win32/ExcludeProc.C may scramble your reports with the goal that you couldn’t open and you need to purchase the secret word. For this situation, if the reports are vital to you, you may’t decline the option. and generally you cannot know when it is carried on, because it may do it under your eyes. In any case, VirTool:Win32/ExcludeProc.C just serves as an instrument for virus and programmers and makes ways for them to get inside and control your entire system. Both are extremely unsafe, yet repulsive.
In this manner, we may recommend you to remove VirTool:Win32/ExcludeProc.C from now on. In the event that you have no clue how to do it, please refer to the removal guides here.
Problems caused by VirTool:Win32/ExcludeProc.C
- Excessive of banner ads, text ads, and spam alert popups.
- Slow operation responding and sluggish system performance.
- Unpermitted change on homepage and search engine.
- Constant system crash due to overly use of CPU.
- Invasion of unknown and malicious programs.
- Identity theft due to hacker’ attack.
VirTool:Win32/ExcludeProc.C Removal Process
Part 1. Manually Remove VirTool:Win32/ExcludeProc.C on Windows OS
Part 1. Manually Remove VirTool:Win32/ExcludeProc.C on Windows OS
(Some of the steps will likely require you to exit the page. Bookmark it for later reference.)
Step 1 – Uninstall malicious programs from Control Panel.

- 1. Press “Windows key + R key” together to open Run window
- 2. Input “control panel” in Run window and hit Enter key to open Control Panel
- 3. Click Uninstall aprogram:
- 4. Right-click programs which may be related with VirTool:Win32/ExcludeProc.C and click Uninstall:
Step 2 – Remove malicious extensions from web browsers.
( NOTE – Please Bookmark This Page because some operations may restart or close your system or web browser )
Chrome

On Chrome: Launch up Google Chrome> click Chrome menu > click Tools> click Extension> select extensions which may be related with VirTool:Win32/ExcludeProc.C> click trash bin
Firefox

On Firefox: Open Firefox, navigate to browser menu in the top right > select Add-ons > select add-ons which may be related with VirTool:Win32/ExcludeProc.C> remove it with Disable or Remove button.
Internet Explorer

On IE: Open Internet Explorer >click Tools > click Manager Add-on Tools and Extensions> select extensions which may be related with VirTool:Win32/ExcludeProc.C > click Remove or Disable button.
Microsoft Edge
On Microsoft Edge: (Reset default homepage and search engine to remove VirTool:Win32/ExcludeProc.C associated hijacker)
( NOTE – Please Bookmark This Page because some operations may restart or close your system or web browser )
Reset Edge homepage: Click More (…) > click Settings > select A specific page or pages under “Open with” > select Custom to type your favorite website.
Reset Edge search engine: Click More (…) > click Settings > Click View advanced settings > Click <Add new> under “Search in the address bar with”> type your favorite search engine >click Add as default.
Step 3 Find and remove malicious registry entries of VirTool:Win32/ExcludeProc.C or malicious program.
Note – In case any suspicious files, unwanted program, unwanted browser extension, or unwanted search engine cannot be removed manually , it is often caused by malicious program, which may adds files to registry or make changes in registry . Therefore, to uninstall such stubborn items, you need to find and remove malicious files in the Registry Editor. Check the steps below:
1. Press “Windows key + R key” together to open Run window;
2. Input “regedit” in Run window and hit Enter key to open Registry;

3. Click Edit menu and select Find >> Type virus’s name into it and click Find Next >> Right click on the files and click Delete ( Only If you can determine that they are related with malware):

Step 4 – Disable Notifications of suspicious websites on Web Browsers.
If some unwanted pop-ups or ads still appear on web browser, please try to disable their Notifications on all web browsers:
On Microsoft Edge
- Launch Edge browser
- Click on menu button of Microsoft Edge
- Click Settings
- Click “View advanced settings”
- Click “Manage” under “Website permissions”
- Find the unwanted URL and click the X (Clear) button to remove the URL.
Chrome
On Google Chrome
- Click the three-dots Menu button on the right upper corner
- Click “Settings” >> Scroll down to the bottom and click “Advanced“
- Click on “Content settings” in the Privacy and Security section
- Click “Notifications“
- Find the unwanted URL >> Click the three dots next to the URL >> click “Block” or “Remove“
Firefox
- Launch Firefox
- Click the Menu button (three bars) on the right upper corner >> Select “Options“
- Click on “Privacy & Security” on the left hand side of the screen
- Scroll down to the “Permissions” >> Click the “Settings” button next to “Notifications”
- Find the unwanted URL >> Click the drop-down menu and select “Block“
On Internet Explorer
- Launch IE
- Click the Gear button on the right upper corner >> Select “Internet options”
- Click “Privacy” tab and click “Settings” under “Pop-up Blocker” section
- Find the unwanted URL and Click the “Remove” button
NOTE – If the instructions above do not work, please download SpyHunter Anti-malware to scan entire system.
Step 5 (Optional) – Reset Web Browser Settings
On Microsoft Edge
- Click the three horizontal dots icon >> Select Settings.
- Click the “Choose what to clear” button
- Click Show more >> Select everything >> click the “Clear” button.
Chrome
On Google Chrome
- Click the Chrome menu icon >> Select Settings
- Scroll down to the bottom and click the Advanced
- Scroll down to the bottom >> Click the Reset button
Firefox
- Click the Firefox menu at the top right corner >> click Help
- Select Troubleshooting Information
- Click the “Refresh Firefox” button
On Internet Explorer
Click on the gear icon >> Click “Internet Options”
Select the “Advanced” tab >> Click “Reset”button
NOTE – If the instructions above do not solve your problems, please download SpyHunter Anti-malware to scan entire system.
Part 2. Manually Remove VirTool:Win32/ExcludeProc.C on Mac OS
(Some of the steps will likely require you to exit the page. Bookmark it for later reference.)
Step 1.Quick malicious process.
- Click the Go button and select Utilities folder;
- Locate the Activity Monitor icon on the screen and double-click on it
- Under Activity Monitor, find a suspicious-looking process, select it and click Quit Process
- A dialog should pop up, asking if you are sure you would like to quit the troublemaking process. Select the Force Quit option
Step 2.Uninstall malicious programs from Mac.

Open the Finder >> Go to the Applications folder >> Find out malicious apps and Click Move to Trash >> Enter your password if requested.
Step 3. Delete malware-generated files in the following folders:
/Library/LaunchAgents folder;
Library/Application Support folder;
/Library/LaunchAgents folder;
/Library/LaunchDaemons folder;
/Library/LaunchAgents
– In Finder, choose “Go” then click on “Go to Folder“:

– In the Go to Folder… bar, type: /Library/LaunchAgents:

In the “LaunchAgents” folder, look for any recently-added suspicious files and move them to the Trash. Here are some examples of malicious files generated by malware:
VirTool:Win32/ExcludeProc.C, “com.VirTool:Win32/ExcludeProc.CDaemon”, “com.VirTool:Win32/ExcludeProc.C, “com.VirTool:Win32/ExcludeProc.C.plist”, “com.adobe.fpsaud.plist” “installmac.AppRemoval.plist”, “myppes.download.plist”, “mykotlerino.ltvbit.plist”, etc.

Library/Application Support
– In Finder, choose “Go” then click on “Go to Folder“:
– In the Go to Folder… bar, type: Library/Application Support:
In the “Application Support” folder, look for any recently-added suspicious files and move them to the Trash. Here are some examples of malicious files generated by malware:
VirTool:Win32/ExcludeProc.C, “com.VirTool:Win32/ExcludeProc.CDaemon”, “com.VirTool:Win32/ExcludeProc.C, “com.VirTool:Win32/ExcludeProc.C.plist”, “com.adobe.fpsaud.plist” “installmac.AppRemoval.plist”, “myppes.download.plist”, “mykotlerino.ltvbit.plist”, etc.
– In Finder, choose “Go” then click on “Go to Folder“:
– In the Go to Folder… bar, type:
In the “LaunchAgentst” folder, look for any recently-added suspicious files and move them to the Trash. Here are some examples of malicious files generated by malware:
VirTool:Win32/ExcludeProc.C, “com.VirTool:Win32/ExcludeProc.CDaemon”, “com.VirTool:Win32/ExcludeProc.C, “com.VirTool:Win32/ExcludeProc.C.plist”, “com.adobe.fpsaud.plist” “installmac.AppRemoval.plist”, “myppes.download.plist”, “mykotlerino.ltvbit.plist”, etc.
/Library/LaunchDaemons
– In Finder, choose “Go” then click on “Go to Folder“:
– In the Go to Folder… bar, type: /Library/LaunchDaemon:
In the “LaunchDaemon” folder, look for any recently-added suspicious files and move them to the Trash. Here are some examples of malicious files generated by malware:
VirTool:Win32/ExcludeProc.C, “com.VirTool:Win32/ExcludeProc.CDaemon”, “com.VirTool:Win32/ExcludeProc.C, “com.VirTool:Win32/ExcludeProc.C.plist”, “com.adobe.fpsaud.plist” “installmac.AppRemoval.plist”, “myppes.download.plist”, “mykotlerino.ltvbit.plist”, etc
Step 4. Delete malicious extensions From Safari / Chrome / Firefox.
Safari

Open Safari >> Click Safari menu button and choose Preferences >> Select the Extensions tab >> Select the suspicious extension and click Uninstall.
Firefox

Open Firefox >> Click the menu button >> select Add-ons >> Determine the suspicious or unwanted extension, click the Disable or Remove button.
Chrome

Run Chrome >> Click the three-dot menu button in the upper-right corner >> Select the More Tools >> Click Extensions >> Determine the suspicious or unwanted extension, click on the Trash icon >> Click Remove
Step 5. Use Combo Cleaner to re-diagnose your Mac and see if it is 100% clean:
To make sure that your system is not infected at all, it’s better to run a scan with Combo Cleaner Antivirus and see if it will detect any remaining unwanted items:
More information about Combo Cleaner, steps to uninstall, EULA, and Privacy Policy. Free scanner checks if your computer is infected. To remove malware, you’ll need to purchase the full version of Combo Cleaner.
– Once combocleaner.dmg installer is downloaded, double-click it to install;
– Then launch Combo Cleaner and click “Start Combo Scan” button;
– Combo Cleaner will scan your Mac for malware infections. Once the scan is completed, remove any found infections.
Remove VirTool:Win32/ExcludeProc.C Today (Apr. 2022 Guide)
VirTool:Win32/ExcludeProc.C is a complicated Trojan horse designed to do harm on thousands of computers. Its appearance is a sign to notice computer users that the security on the operating system has been compromised. Consisted of multiple components, VirTool:Win32/ExcludeProc.C is cunning to conceal on computer furtively, which makes the removal much complicated.
While doing online activities, users must be highly cautious with every suspicious resource. In general, VirTool:Win32/ExcludeProc.C is known to take the advantage of malicious link, pop-up ads, porn site, untrustworthy update website, removable device and other similar threat to penetrate into computer surreptitiously. It is better to upgrade the antivirus program into the latest version timely.
VirTool:Win32/ExcludeProc.C is such an aggressive virus that the impact it lays would extend to a large fields. In general, the registry entry, system file, memory space, program and security defense are all the targets to be attacked by VirTool:Win32/ExcludeProc.C. Even worse, it may bring in other threats to collect private information for online banking portals and social media. Without any doubt, VirTool:Win32/ExcludeProc.C is a dangerous virus to destroy your computer it must be removed as quickly as possible.
How to Remove VirTool:Win32/ExcludeProc.C? (Windows + Mac OS)
Quick Menu
Section A – VirTool:Win32/ExcludeProc.C Removal Steps For Windows OS
Section A – VirTool:Win32/ExcludeProc.C Removal Steps For Windows OS
( NOTE – Please bookmark this page first, because some steps will require you to restart your web browser or computer. )
Step 1. End malicious process run by VirTool:Win32/ExcludeProc.C and related malware.
1. Hit Ctrl + Shift + Esc keys at the same time to open Windows Task Manager:
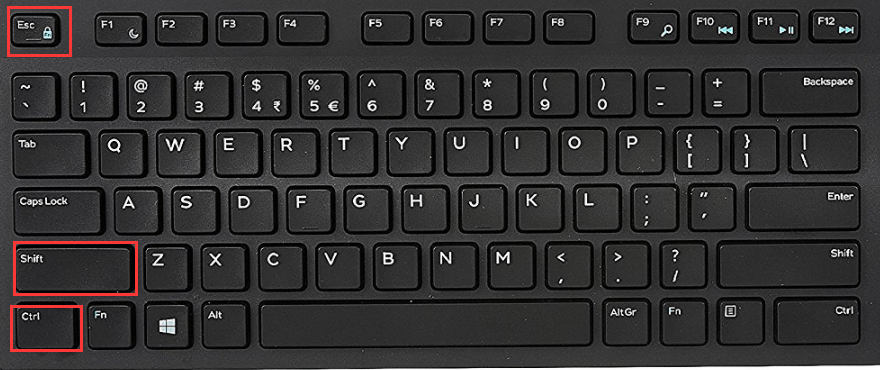
2. Find malicious process related with VirTool:Win32/ExcludeProc.C or malware, and then right-click on it and click End Process or End Task.

Step 2. Uninstall malicious programs related with VirTool:Win32/ExcludeProc.C.
Press “Win + R ” keys together to open the Run screen;

Type control panel in the Run window and click OK button;

In Control Panel, click Uninstall a program under Programs;

Look for malicious app related with VirTool:Win32/ExcludeProc.C; Right-click on the malicious program and click Uninstall.

Many malware may re-install themselves multiple times if you don’t delete thier core files. To get rid of VirTool:Win32/ExcludeProc.C completely, we recommend downloading SpyHunter Aniti-malware to scan entire system and delete all malicious files .
Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. Read our EULA, Privacy Policy, Cookie Policy . See more Free SpyHunter Remover details.
Step 3. Delete extension installed by VirTool:Win32/ExcludeProc.C and related malware.
Chrome
On Chrome
Click the Chrome menu button >> Click Tools >> Select Extensions:

Find extension that may be related with VirTool:Win32/ExcludeProc.C or potential threat >> Click the trash can icon to delete them.

Microsoft Edge
On Microsoft Edge
Start Edge: Click the More (…) button ahe tog right corner and click Extensions:

Select the extensions you want to remove and click Remove:


Firefox
On Firefox
Click the menu button and choose Add-ons. The Add-ons Manager tab will open.

In the Add-ons Manager tab, select the Extensions panel >> find extension that may be related with VirTool:Win32/ExcludeProc.C or potential threat >> Click Remove button.

On Internet Explorer
Open the IE, click the Tools button , and then click Manage add-ons.

Choose Toolbars and Extensions on left side of the window >> Find extension that may be related with VirTool:Win32/ExcludeProc.C or potential threat>> Click Disable button

Malicious extensions may re-install itself on web browser if you don’t delete core files of VirTool:Win32/ExcludeProc.C and related malware. To get rid of VirTool:Win32/ExcludeProc.C completely, we recommend downloading SpyHunter Aniti-malware to scan entire system and delete all malicious files .
Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. Read our EULA, Privacy Policy, Cookie Policy . See more Free SpyHunter Remover details.
Step 4. Remove malicious files created by VirTool:Win32/ExcludeProc.C or related malware.
1. Hit Windows + R keys at the same time to open Run window and input a regedit and click OK:

2. In the Registry Editor, hit Windows key + F key together to open Find window → Enter virus name → Press Enter key to start search.

3. When the search is completed, right click the folders related with VirTool:Win32/ExcludeProc.C and click Delete button:

Please Read This Before You Remove Registry Files
PLEASE Be Carefully, Do Not Delete Healthy Registry Entries, Or Your Computer May Be Damaged.
If you are not able to determine which regsitry files are malicious, we recommend downloading SpyHunter Anti-malware to scan entire system and find out all malicious files. It can avoid mistakes and may reduce the cleanup time from hours to minutes.
Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. Read our EULA, Privacy Policy, Cookie Policy . See more Free SpyHunter Remover details.
Step 5. Reset Web Browsers to remove Hijackers Brought by VirTool:Win32/ExcludeProc.C.
Chrome
Reset Chrome:
- Click the Chrome menu button, represented by three horizontal lines;
- Click Settings when the drop-down menu appears;
- In the Settings screen, scroll to the bottom of the page and click on the “Advanced” link;
- Click on the “Reset settings to their original defaults” button.
- A confirmation dialog appears, click on the “Reset Settings” button.
Reset Microsoft Edge:
- Click on Microsoft Edge’s main menu button, represented by three horizontal dots;
- Click on “Settings“ button when the drop-down menu appears;
- Click on “Reset Settings”On the left side of the window;
- Click on “Restore settings to their default values”
- Click on the “Reset” button in the new confirmation window that opens.
Firefox
Reset Firefox:
- Click the menu button of firefox, represented by three horizontal lines;
- Click on “Help“ button when the drop-down menu appears;
- Click on “Troubleshooting Information“ from the Help menu;
- Click the “Refresh Firefox” button in the upper-right corner of the “Troubleshooting Information” page.
- Click on the “Refresh Firefox” button in the new confirmation window that opens.
Reset IE :
- Open Internet Explorer, click on the gear icon in the upper-right part of your browser, then select “Internet Options“.
- Now select the “Advanced” tab, then click on the “Reset” button
- In the “Reset Internet Explorer settings” section, select the “Delete personal settings” checkbox, then click on the “Reset” button.
NOTE – If the steps above doesn’t help, please rescan entire infected PC with Spyhunter anti-malware and let it help you fix all problems.
Section B – VirTool:Win32/ExcludeProc.C Removal Steps For Mac OS
Step 1 – Remove nasty extension and browser hijacker related with VirTool:Win32/ExcludeProc.C or malware.
Chrome
– Click the setting button “≡” at the top right of the browser window, choose “More Tools” and choose “Extensions“.

– Click the “trash can icon” button to remove extension related with VirTool:Win32/ExcludeProc.C or malware:

Safari
Safari:
– Choose Safari > Preferences

– On the ‘Extensions’ tab, find out the extension related with adware or hijacker and click Uninstall or Disable

Firefox
Mozilla Firefox:
– Click the settings button (three horizontal bars) in the top-right corner and then select ‘Add-ons’.

– Click “Extensions” tab under Add-on Manager page to view the extensions.
– Find the suspicious add-on you want to disable and click its “Disable” button.
– If you want to delete an extension entirely, click “Remove.”

Malicious browser extensions hijack your Google Search and redirect you to unwanted websites. To get rid of related search hijacker, you need to delete core files of VirTool:Win32/ExcludeProc.C and related malware. We recommend downloading SpyHunter Mac Antimalware to remove all malicious apps and hijacker for you. This may save you hours and ensure you don’t make mistakes that harm your system
Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. Read our EULA, Privacy Policy, Cookie Policy . See more Free SpyHunter Remover details.
Step 2 – Uninstall harmful Apps related with VirTool:Win32/ExcludeProc.C or malware
– Open Finder at the Dock

– Select Applications and find out suspicious apps related with VirTool:Win32/ExcludeProc.C , then right click on the app and click Move to Trash:

– Right click on Trash icon to select Empty Trash

Step 3 – Remove malicious files generated by VirTool:Win32/ExcludeProc.C or malware from your Mac
Malware geneates lots of malicious files and folders on infected Mac, to avoid VirTool:Win32/ExcludeProc.C reinstalling itself, you need to find out and remove all malicious files:
1. Click the Finder icon from the menu bar >> choose “Go” then click on “Go to Folder“:

2. In the Go to Folder… bar, type “/Library/LaunchAgents” and click Go:

3. In LaunchAgents folder, search for any recently-added suspicious files and move them to the Trash.

Here are some examples of files generated by malware:
“installmac.AppRemoval.plist”, “com.genieo.completer.download.plist” “com.genieoinnovation.macextension.plist” “com.genieo.engine.plist” “com.adobe.fpsaud.plist” , “myppes.download.plist”, “mykotlerino.ltvbit.plist”
4.Repeat the process on the following folders:
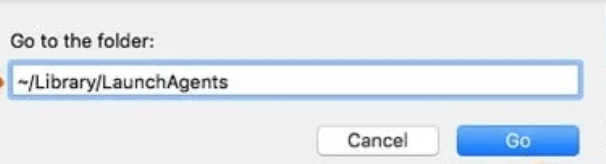
/Library/Application Support

/Library/LaunchDaemons
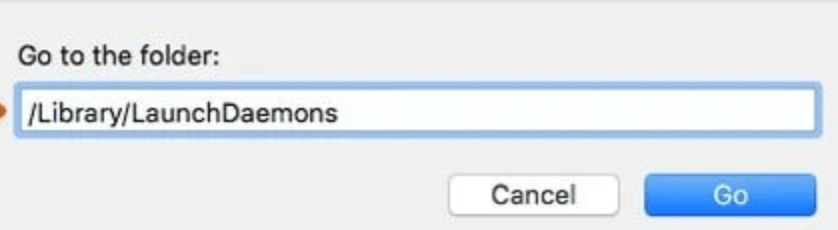
Many malware may re-install themselves multiple times if you don’t delete thier core files. To find and remove all malicious files , We recommend downloading SpyHunter Mac Antimalware to scan your Mac. This may save you hours and ensure you don’t make mistakes that harm your system
Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. Read our EULA, Privacy Policy, Cookie Policy . See more Free SpyHunter Remover details.
Step 4 – Download SpyHunter Antimalware For Mac to Scan For Malicious Apps and Files.
Lots of Malware keep generating malicious files on infected computer deeply, thus it’s quite difficult for common computer users to find out and remove all harmful items related with VirTool:Win32/ExcludeProc.C. Meanwhile, there will be possibility that users remove core system files by mistake and then the entire computer will be harmed seriously.
To avoid the risks, We recommend all users downloading SpyHunter Antimalware For Mac, a professional automatic malware removal tool which keeps your Mac away from virus and malware attack and avoid online spam and phishing websites and protect your privacy and files well.
1. Click Download button here to download SpyHunter For Mac :
(Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. Read itsEULA, Privacy Policy See more Free SpyHunter Remover details.)
2. Double-click SpyHunter-1.2-15-7043-Installer.dmg to install Spyhunter For Mac:

3. Once SpyHunter For Mac is installed, run a scan and register its full version to remove all malicious objects on your Mac.

4. In case VirTool:Win32/ExcludeProc.C is still infecting your Mac, Submit a Support Ticket and the support agent will conact to help you.
Way to Remove VirTool:Win32/ExcludeProc.C (Apr. 2022 Updated Guide)

VirTool:Win32/ExcludeProc.C is a part of the infamous Trojan horse family of viruses. Once inside the system, the VirTool:Win32/ExcludeProc.C and related spyware may collect your data and information until it has gathered enough information to ruin your day.
Since VirTool:Win32/ExcludeProc.C is a particularly nasty piece of malware, the easiest way to propagate the virus is to litter it throughout compromised websites, corrupted links, spam emails and even on fake news posts on social media. Once users click these links or visit such websites, it’s already too late- the virus will have found a way to sneak itself onto your system by posing as safe data, bypassing most antivirus and browser security! Other methods of catching the VirTool:Win32/ExcludeProc.C Trojan include downloading illegal torrents; movies, music, games or pornography are the most pirated media on the internet, so it makes sense for hackers to place these files as a kind of bait, whilst hiding the Trojan application inside the torrent file.
VirTool:Win32/ExcludeProc.C plants a Trojan virus in the first convenient place that it can find, it doesn’t matter where it installs itself; since all it needs to do is register every key press that you make on your computer. This is a very scary prospect, since it will then forward the information back to the hacker, giving them potential access to: Logins and passwords for your social media, online shopping, PayPal, online banking and anything else that uses a written username and password.
Any time that you make a search, write an email, an instant message or write in a text document, the VirTool:Win32/ExcludeProc.C is sitting and recording it all, ready to send it to the hacker.
As you can see, VirTool:Win32/ExcludeProc.C is a very nasty virus, and once the hacker has access to this information, they can either contact you, to make ransom demands for your information (from which they will take your money and continue to sell or use your information for their own ends- these people are ruthless criminals.)
Remove VirTool:Win32/ExcludeProc.C from Windows OS PC (Steps)
(If have Virus / Malware on Mac OS , Please Use This Guide – How to Remove Virus & Malware From Mac . )

Solution A – Malware Automatic Removal (Simple and Safe For All Users)
Solution B – Malware Manual Removal (For Users with Advanced Computer Skills)
Solution A – Malware Automatic Removal
In case VirTool:Win32/ExcludeProc.C has invaded your computer, it is possible that some other virus or malware are brought in as well. It will be a tough and lengthy process if you manually search and remove all core files of malware. And you may even harm your system once you delete crucial system files.
Therefore, to avoid risks and remove VirTool:Win32/ExcludeProc.C efficiently, we recommended using Spyhunter Anti-malware to scan for VirTool:Win32/ExcludeProc.C and remove related malware. It is specialized in preventing all the latest virus & malware and removing threats hiding in a infected computer.
Certifications & Independent Test Reports on SpyHunter 5

1. Download SpyHunter now:
(Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. Read its EULA, Privacy Policy See more Free SpyHunter Remover details.)
2. Double click the SpyHunter-Installer:

– When the “User Account Control” dialog appears, choose “Yes“.

3. Choose your preferable language and click the “OK” button to proceed the installation. Wait several minutes to complete the installation

4. Once the installation is completed, run SpyHunter and click Start Scan Now.

5. When scan is completed, select all detected dangerous items and click Next:

6. If you want SpyHunter to help you remove all detected threats and get the daily system protection from now on, you will need to Register its full version. If the automatic removal does not help, you can get One-on-one customer support to fix your problem from computer experts.

Solution B – Malware Manual Removal
NOTE – Some operations in the removal process may require you to exit this page or restart computer, Please Bookmark This Page first For later reference.
Step 1. Try to find out and end the dangerous processes run by VirTool:Win32/ExcludeProc.C or other threat.
– Press CTRL + SHIFT + ESC keys at the same time to open the Processes Tab in Windows Task Manager:

Try to find out the dangerous processes run by VirTool:Win32/ExcludeProc.C other malware according to the CPU Usage and t he name of its Description :
If a suspicious process is from unknown third party company , meanwhile it is causing High CPU Usage , then this process may be the dangerous process of malware.


If you are’re sure which processes are dangerous, you can select them and click End Process one by one:

Helpful Tips – If you are not able to find the dangerous processes, we recommend downloading SpyHunter Anti-malware to scan for VirTool:Win32/ExcludeProc.C and related malware. SpyHunter is designed to identify, remove and block virus and malware. It may save hours for you and avoid wrong operations:
(Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. Read its EULA, Privacy Policy See more Free SpyHunter Remover details.)
Step 2. Uninstall VirTool:Win32/ExcludeProc.C related apps or other dangerous programs from Control Panel.
– Press Win + R keys at the same time to open the “Run” window >> Then type appwiz.cpl and click OK :


– Now you can see the program list of Control Panel, please check the list and look for dangerous app or suspicious app may be related with VirTool:Win32/ExcludeProc.C. Once you determine the unsafe apps, select them and click Uninstall:

Important Note – If VirTool:Win32/ExcludeProc.C or related program cannot be uninstalled from Control Panel, you may need to remove its core files. We recommend downloading SpyHunter Anti-malware to scan for malicious files and related malware . SpyHunter is a professional and powerful anti-malware program designed to identify, remove and block virus and malware from Windows OS.
(Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. Read its EULA, Privacy Policy See more Free SpyHunter Remover details.)
Step 3. Delete VirTool:Win32/ExcludeProc.C and related extension Adware / Hijacker from web browsers.
NOTE – Some operations in the removal process may require you to exit this page or turn off web browser, Please Bookmark This Page first For later reference.
Remove Browser Hijacker from Microsoft Edge
1. Change Edge’s default search engine to Google Search:
Open Microsoft Edge >> Click the menu button (the button with three dots) at the top-right corner >> Select “Settings” in the menu.

In the “Settings” panel >> Scroll down to Advanced settings and click the “View advanced settings” button.

In the “Advanced settings” panel >> Scroll down to the “Search in the address bar with” setting >> Click the “Change search engine” button.

In the “Change search engine”>> Select Google Search and click “Set as Default”.

2. Change your Homepage on Edge:
– Open Microsoft Edge >> Click the three-dotted menu at the upper-right corner of the windows >> choose Settings.
– Under the Open Microsoft Edge with option >> Choose A specific page or pages from the menu >> Enter a URL into that box and click the save button off to the right.

Chrome
Remove Adware Extension and Hijacker from Google Chrome
1. Delete unsafe or unwanted extension from Chrome:
– Click Chrome menu → select Tools.

– Then click Extension >> Select VirTool:Win32/ExcludeProc.C or unwanted extensions → click on Trash bin >> Click Remove

2. Change your Homepage on Chrome:
Click Chrome menu >> Select Settings ;
Within Settings, in the Appearance section, check the box next to Show Home button;
Click Change next to the address shown below the Show Home Button;
In the window under New Tab Page >> Type in the web address of the page you like to set as your homepage >> Click OK

3. Change your default Search Engine on Chrome:
– Click Chrome menu >> Select Settings ;
– Within Settings, in the Search engine section >> click Manage search engines…
– Choose the search provider you want to make as the default and then click Make default;
– Click Done.
Firefox
Delete Adware Add-on and Hijacker from Mozilla Firefox
1. Delete unsafe or unwanted extension from Firefox:
– Go to Firefox menu and click on Tools >> Select Add-ons

– Select VirTool:Win32/ExcludeProc.C unwanted extensions and add-ons >> Click Disable or Remove button to remove it.

2. Change your Homepage on Firefox:
– Click the menu button and choose Options >> Click the Home panel.
– Click the menu next to Homepage and new windows and choose “enter your own URLs” >> Type in the page you want to set.
3. Change your default Search Engine on Firefox:
– Click the menu button and choose Options
Internet Explorer
Delete Adware Add-on and Hijacker from Internet Explorer
1. Delete unsafe or unwanted add-on from IE:
– Click on Tools >> go to Manage Add-ons

– In Toolbars and Extensions >> Choose VirTool:Win32/ExcludeProc.C or unwanted extensions and add-ons → Click Disable button

2. Change your Homepage on IE:
– Click Tools in the upper-right corner >> Select Internet Options.- Under the General tab, type the URL of the web page you want to set.- Click Apply >> Click Ok.
3. Change your default Search Engine on IE:
– Open Internet Explorer >> click the gear icon >>Click Manage add-ons >> Click Search Providers.
– Now you will see those which are already present on IE. Right-click the one you want to set as your search engine >> select Set as default.

Important Tips – If the above operations cannot remove VirTool:Win32/ExcludeProc.C related extension or hijacker from browsers, you may need to remove cord files of VirTool:Win32/ExcludeProc.C or related malware first. We recommend downloading SpyHunter Anti-malware to scan your PC and find out all malicious items:
(Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. Read its EULA, Privacy Policy See more Free SpyHunter Remover details.)
Step 4. Try to find out and remove VirTool:Win32/ExcludeProc.C related files or other malicious files from Regidit Editor.
1.Press“Windows + R key” together to open Run Windows.
2. Type “regedit” in Run Window and click OK button to open registry.

3. Find and Remove Registry Files created by VirTool:Win32/ExcludeProc.C and other threats:
Click Edit >> Click Find:


Type in virus’ name and click Find Next >> Delete dangerous registry files found.
Important Tips – Do Not Delete Crucial System Files in Regedit Editor by Mistake! Or your computer may be damaged!
Before you delete any registry files, you need to be 100% sure that these files are dangerous items. If You Want To Avoid The Risk, we recommending using SpyHunter Anti-Malware to scan for malicious files:
(Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. Read its EULA, Privacy Policy See more Free SpyHunter Remover details.)
Step 5. Block “Notifications” of Suspicious Websites on Web Browsers.
- Block Microsoft Edge Notifications:
- Click the menu button (three dots) on the right upper corner of the Edge window
- Scroll down, find and click “Settings“
- Scroll down again and click “View advanced settings“
- Click “Manage” under “Website permissions“
- Click the switch under each suspicious website
- Block Chrome Notifications:
- Click the Menu button (three dots) on the right upper corner of the screen
- Select “Settings“, scroll down to the bottom and click “Advanced“
- Scroll down to the “Privacy and security” section, select “Content settings” and then “Notifications“
- Click three dots on the right hand side of each suspicious URL and click “Block” or “Remove“
- Block Firefox Notifications:
- Click the Menu button (three bars) on the right upper corner of the screen
- Select “Options” and click on “Privacy & Security” in the toolbar on the left hand side of the screen
- Scroll down to the “Permissions” section and click the “Settings” button next to “Notifications“
- In the opened window, locate all suspicious URLs, click the drop-down menu and select “Block“
- Block IE Notifications:
- Click the Gear button on the right upper corner of the IE window
- Select “Internet options“
- Select the “Privacy” tab and click “Settings” under “Pop-up Blocker” section
- Select suspicious URLs under and remove them one by one by clicking the “Remove” button
Important Note – If the above operations cannot remove VirTool:Win32/ExcludeProc.C or similar pop-up ads, you may need to find out and remove malicious programs related with it. We recommend downloading SpyHunter Anti-malware to scan entire system and find out all malware:
(Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. Read its EULA, Privacy Policy See more Free SpyHunter Remover details.)